

Replace your legacy Sonar setup with Aikido
Stop writing and maintaining thousands of rules. Aikido gives you 50 checks that cover SonarQube's rules and the gray areas they miss.


SonarQube buries your team in warnings. Aikido fixes them.
Live in minutes
Aikido finds real issues in minutes. SonarQube takes 2 months to roll out to your teams.
Your rules, less noise
Aikido checks changed lines against your rules. SonarQube is known for excessive warnings.
Pay per developer
Aikido's core platform price is per developer. SonarQube charges per line of code, making it difficult to budget for growing codebases.
Aikido vs SonarQube


With Aikido we replaced three services: SonarQube for SAST, the dependency check, and a separate tool for secrets. Now we have everything in one place.
Elizaveta KatiushinaSecurity Engineer
Code quality and security that fit your workflow and fix issues for you
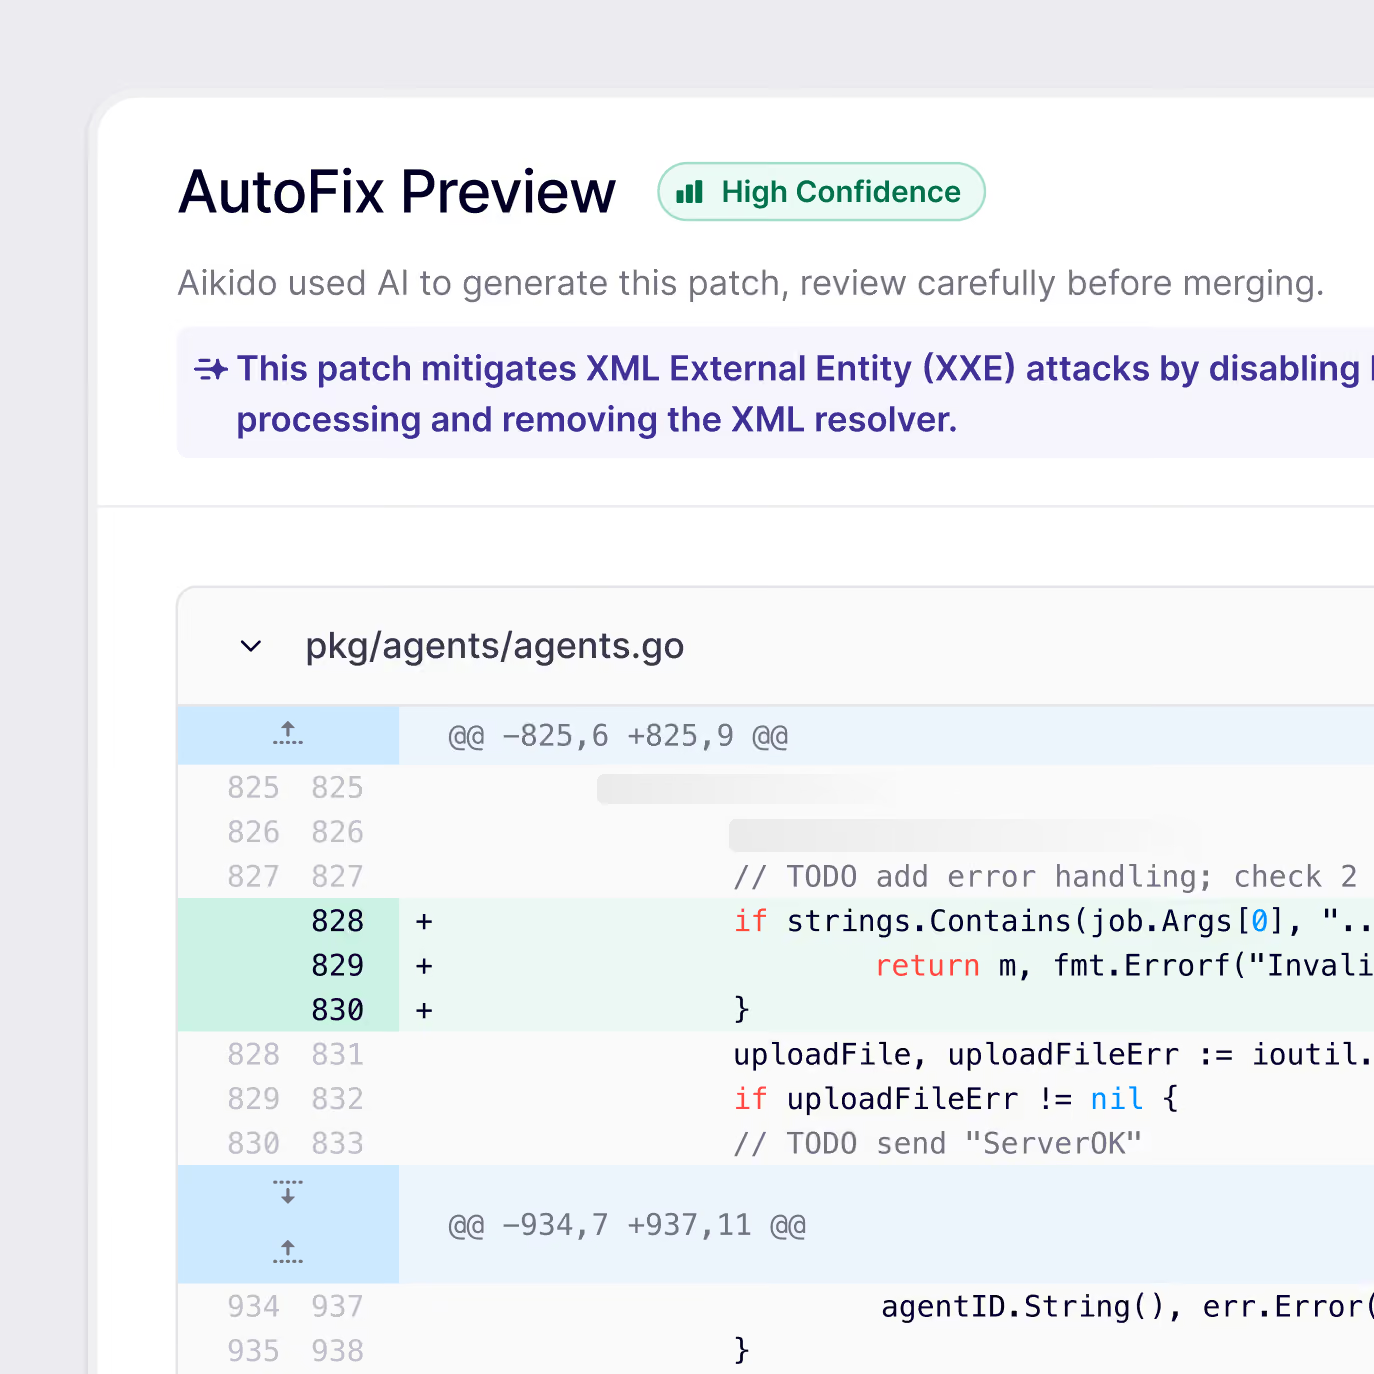
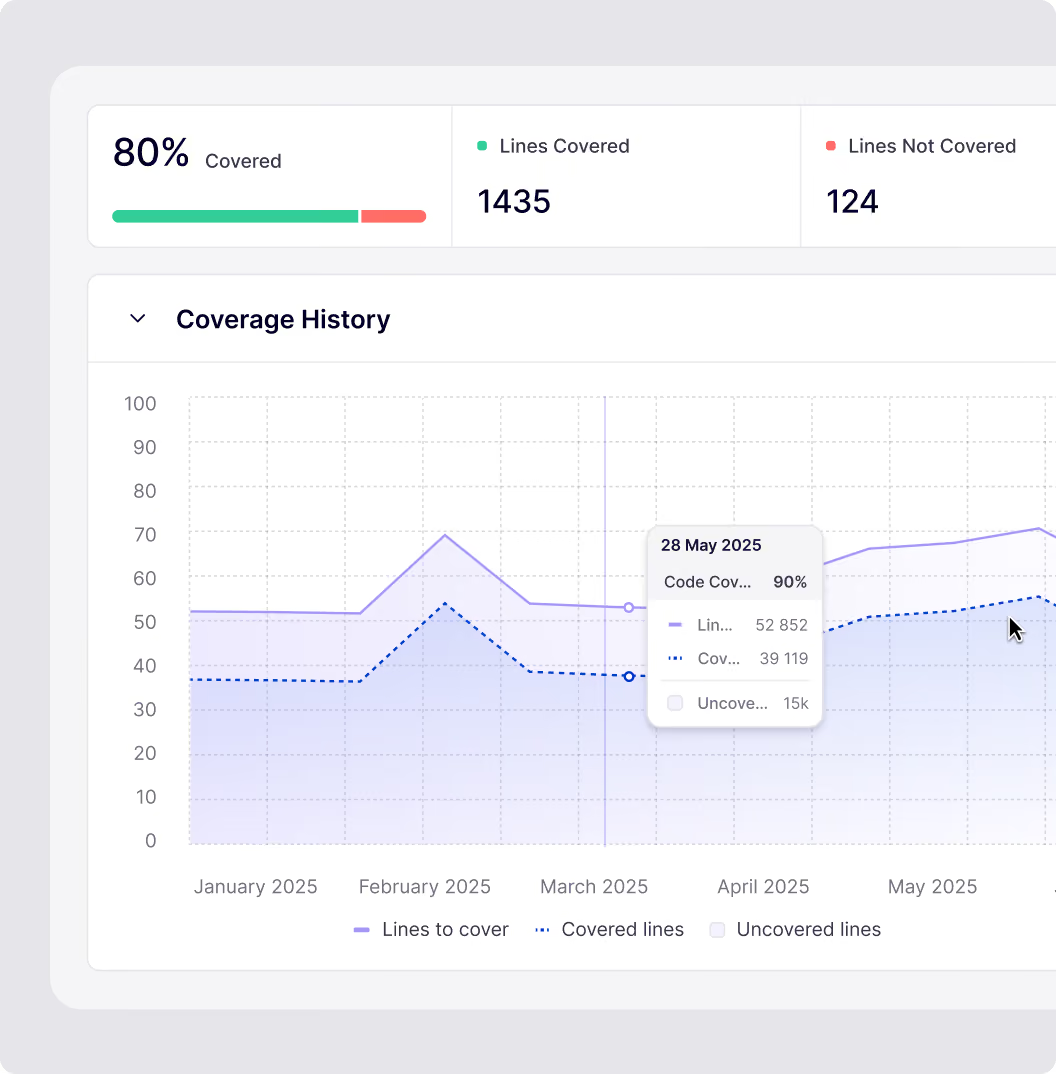
Code Quality beyond the linter
Checks on every PR catch logic bugs, edge cases, and duplicated logic, explained in plain language
Write team rules in plain language, once, across 48 supported languages from COBOL to Zig
Quality gates on every PR: block merges by finding severity or test coverage threshold
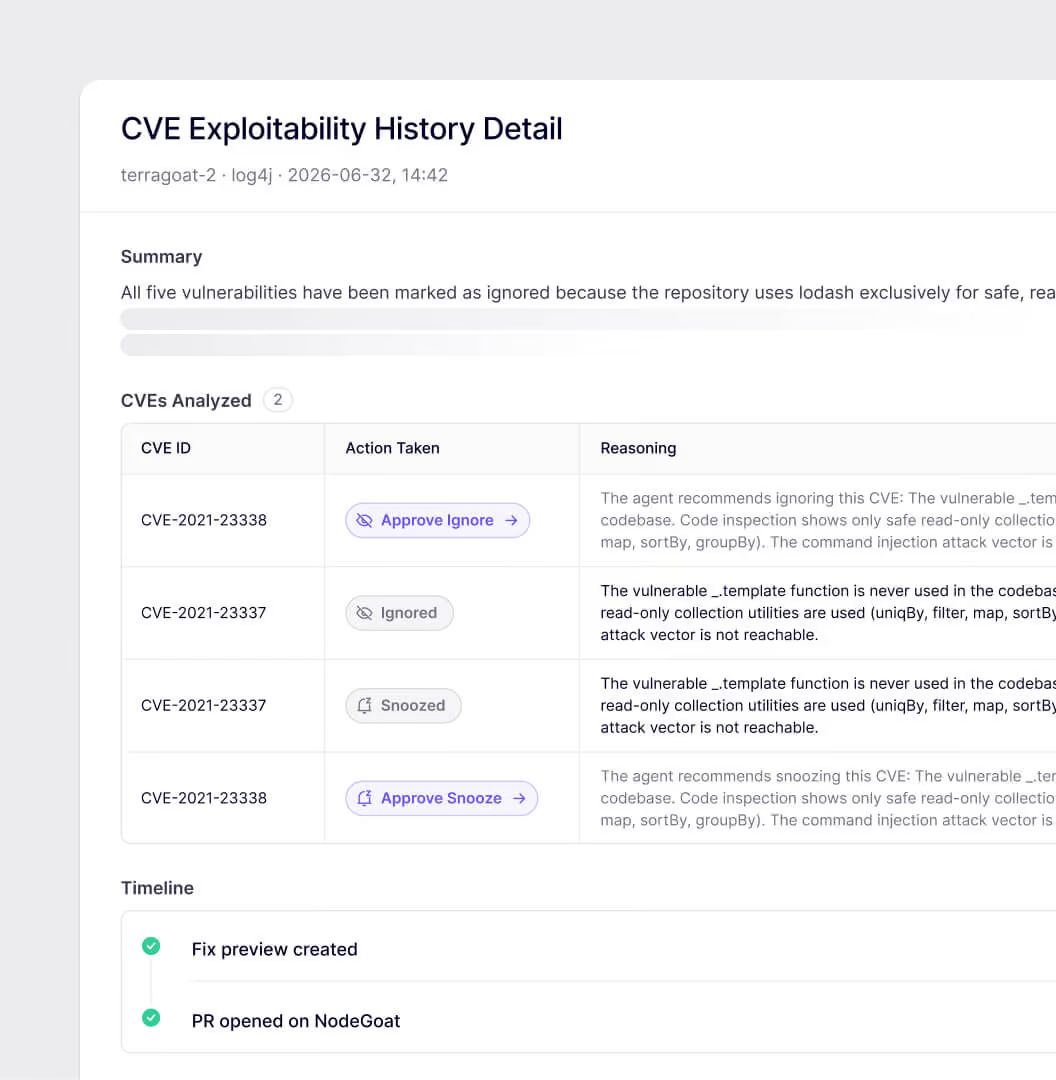
Only see what is important
AutoTriage weighs reachability, exploitability, and code context before issues reach your queue
CVE exploitability analysis checks whether vulnerable dependencies are exploitable in your environment, not just present in a lockfile
Secrets AutoTriage prioritizes exposed secrets by status and privilege
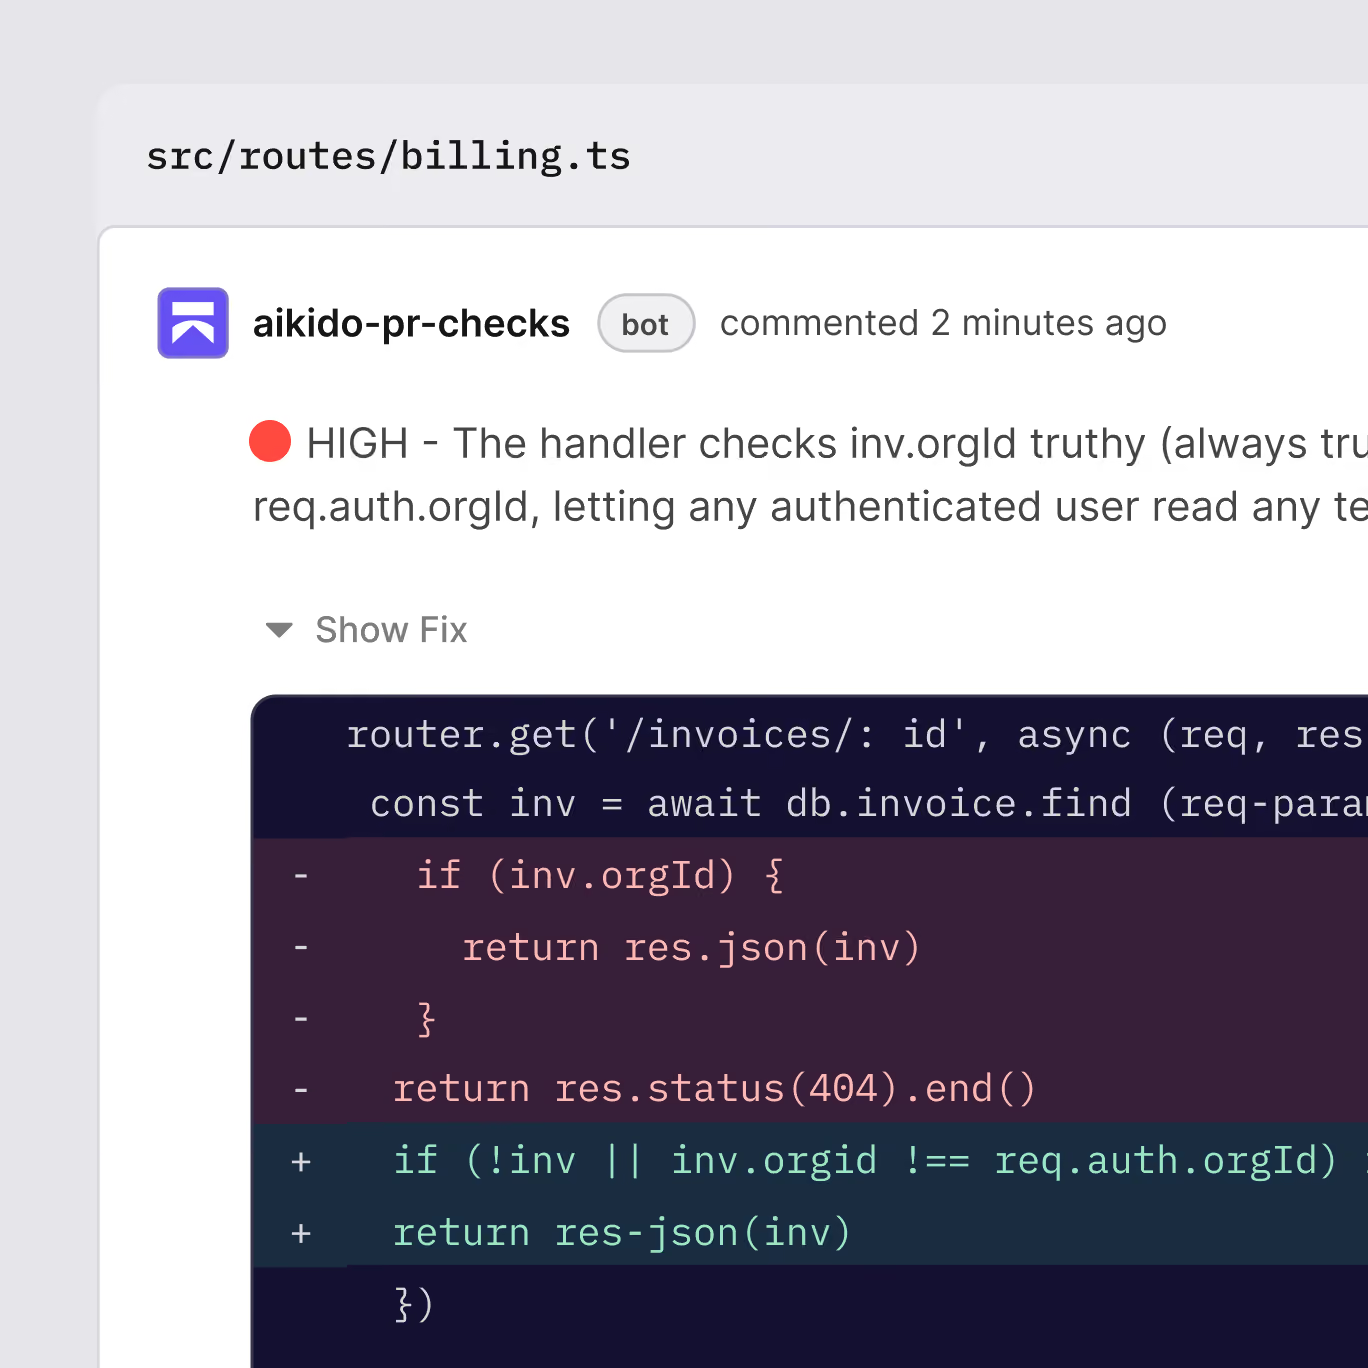
Why teams leave SonarQube for Aikido
Too many warnings
False positives and excessive warnings that still require manual triage.
Never-ending tuning
SonarQube has complex configuration and rule tuning that takes significant effort on large projects.
Waiting on support
G2 reviews consistently rate Aikido's support higher than SonarQube.

"There's no other vendor we've worked with that communicates so much and actually cares about what we say."
Angel IndzhovHead of Cybersecurity at Reward Gateway

"For me the answer is reachability. It shows what actually has to happen to exploit something, so you know which vulnerability is really going to be a problem. That was golden."
Angel IndzhovHead of Cybersecurity
Built for devs. Trusted by security.
For Developers
For Security Teams
For CISOs
Get secure today,
quickly and for free.
Secure your code, cloud, and runtime in one central system. Connect a repo to discover what the reasoning agents find in your codebase.


